Security questionnaire automation
A security questionnaire, answered from evidence you already approved
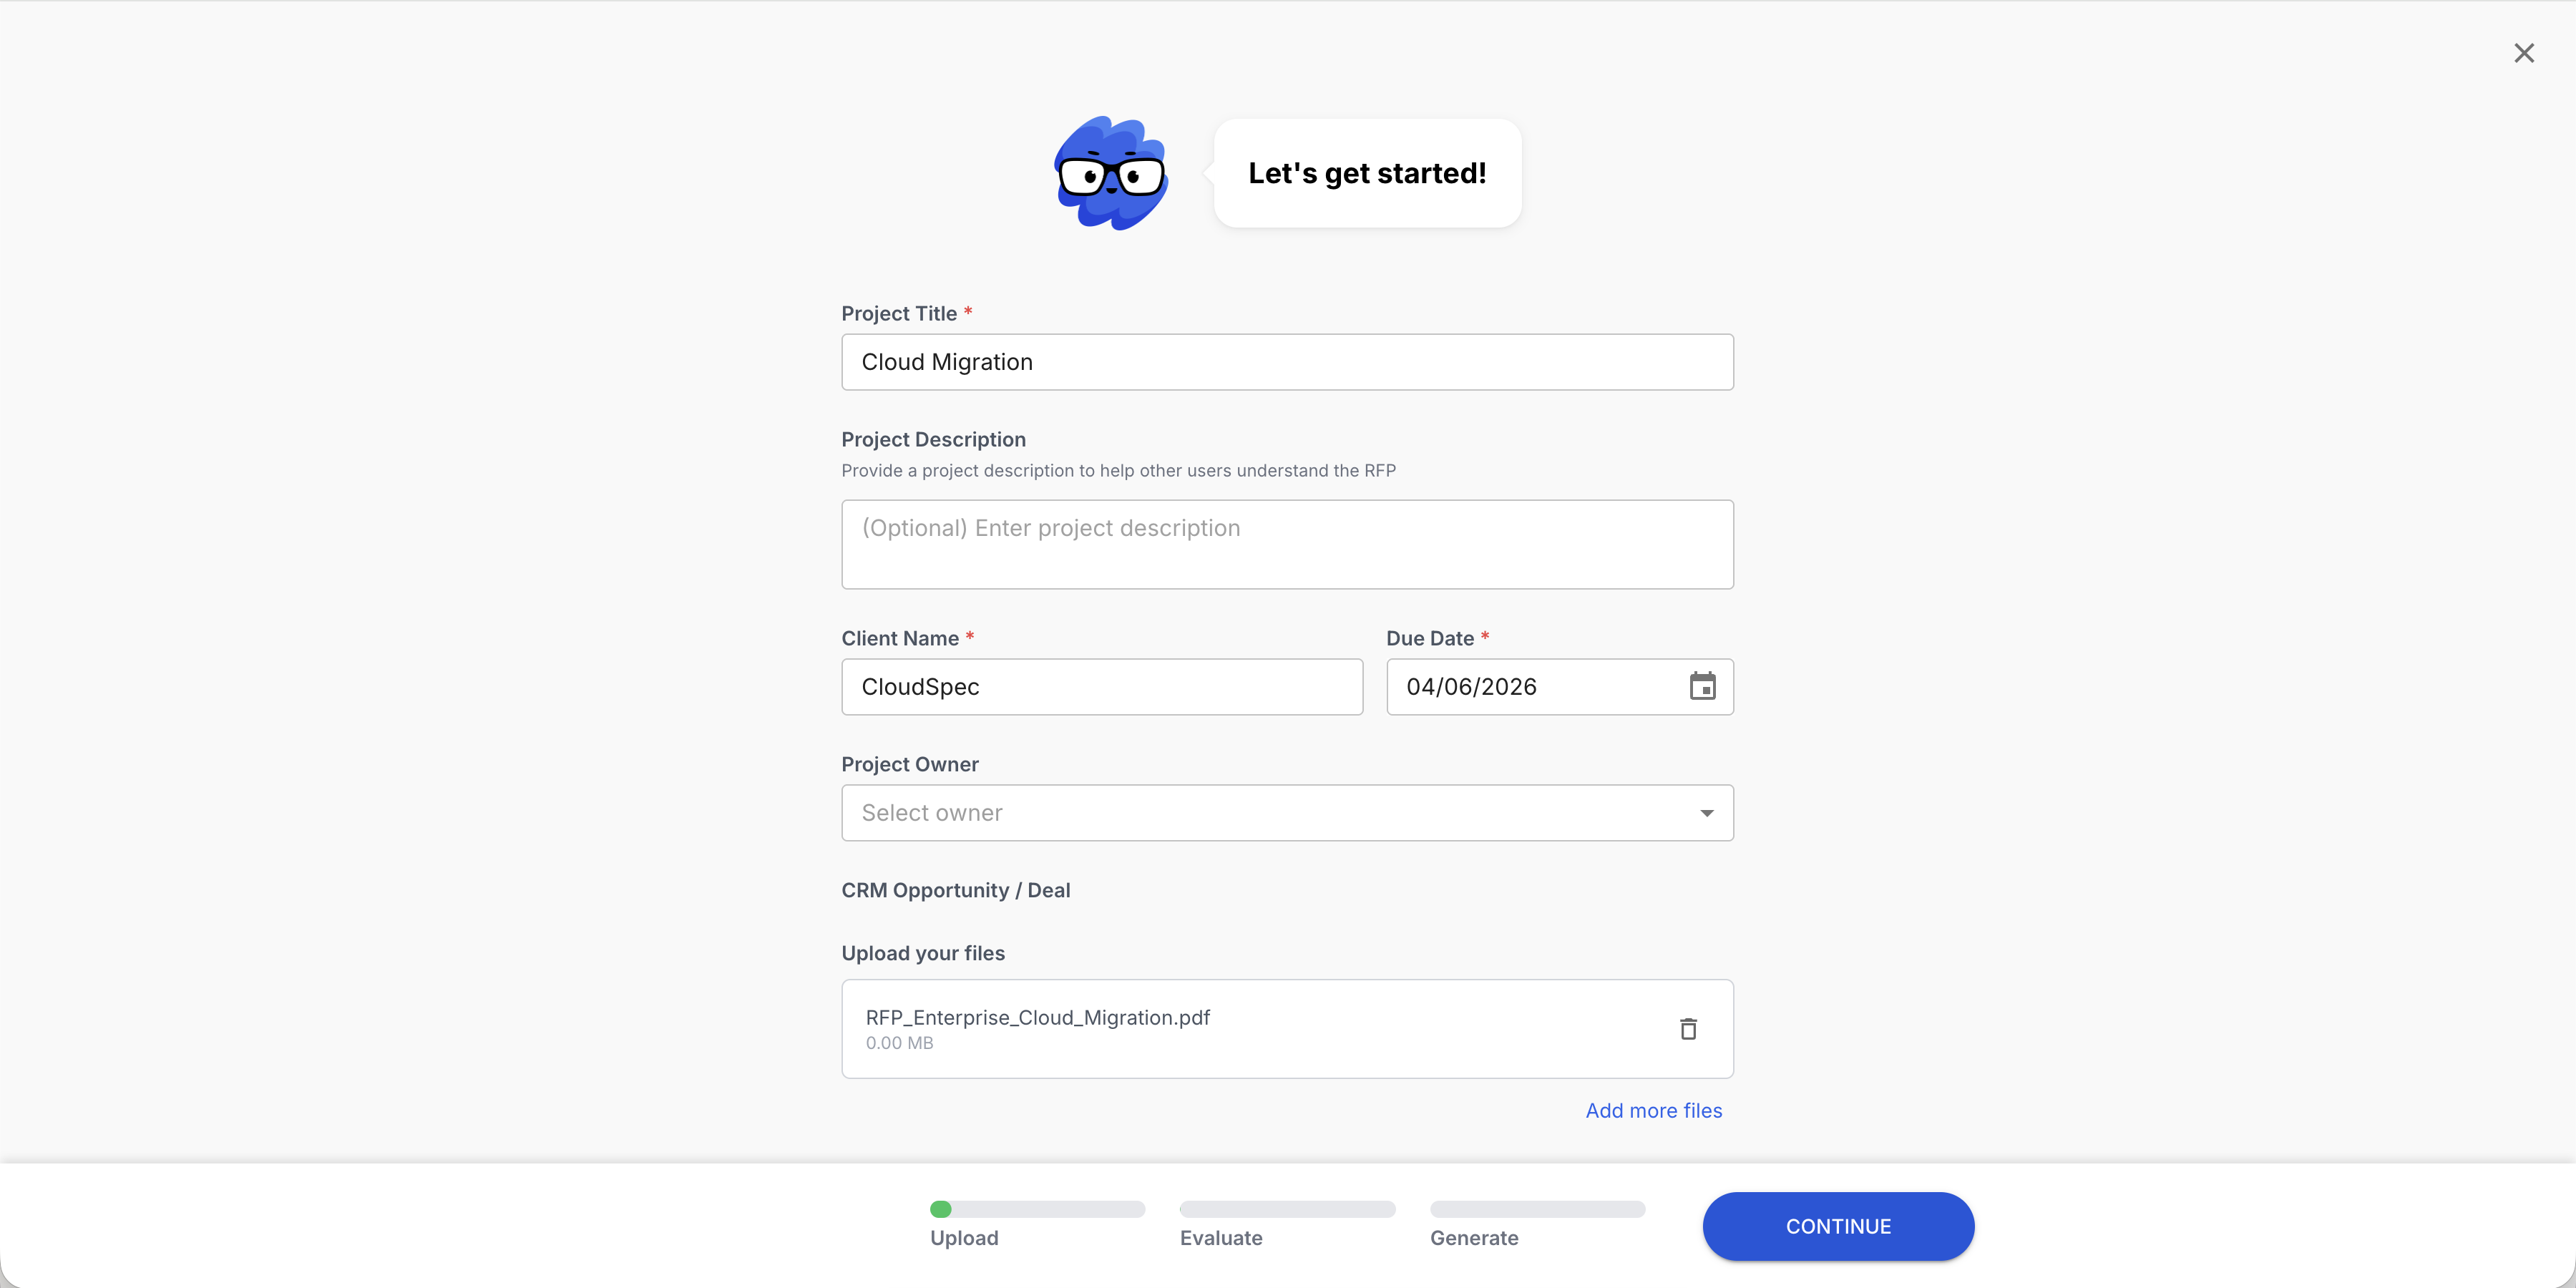
This page is the workflow rather than the pitch: what happens to a SIG, a CAIQ or a buyer's own spreadsheet between the file arriving and the answers going back, who touches it, and where it reads your evidence from.
What happens between the file landing and the answers going back
Five steps. Your security team only really works in the fourth one. The fifth is the one that stops two answers contradicting each other in front of a buyer.
- 01
Intake, any format
SIG Lite, SIG Full, CAIQ, VSA, a spreadsheet, a document, a portal export. Whatever the file is, Tribble reads the questions out of it and sorts them by control area.
- 02
Retrieval from approved evidence
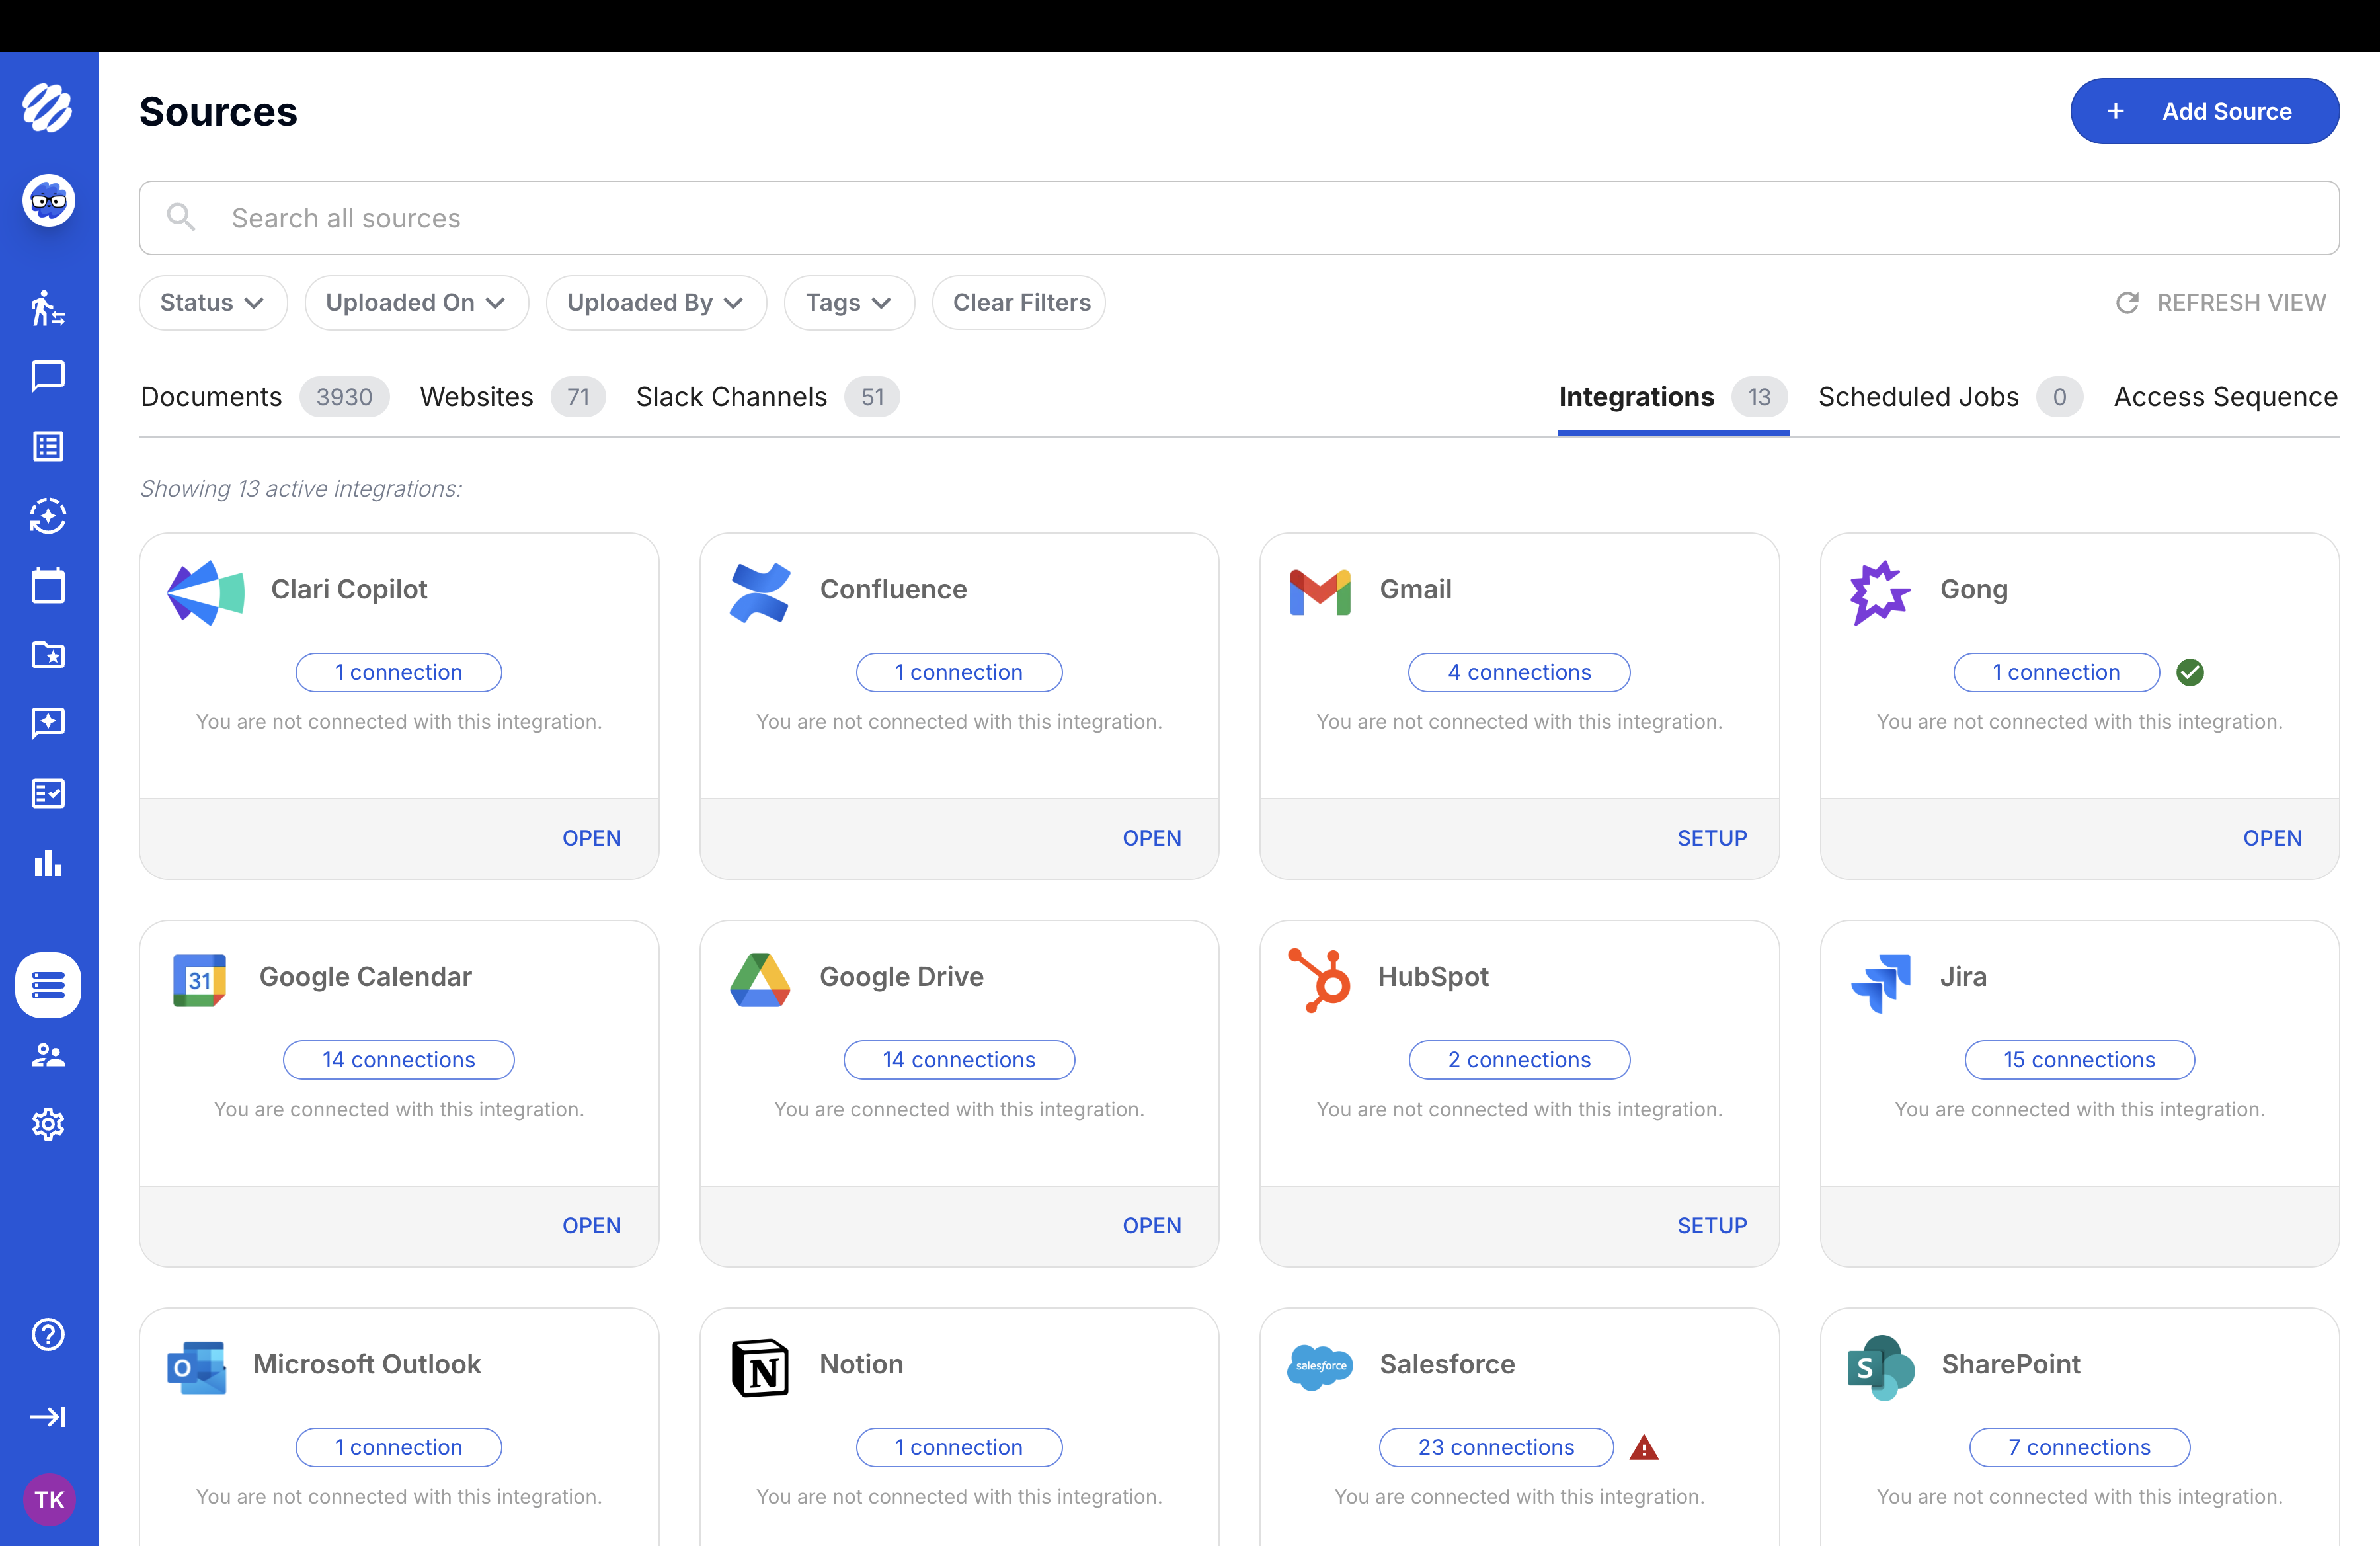
Each question goes to your approved content: policies, SOC 2 evidence, certification scope, the answers you gave last time. Nobody sees evidence they could not already open themselves.
- 03
A draft with the source attached
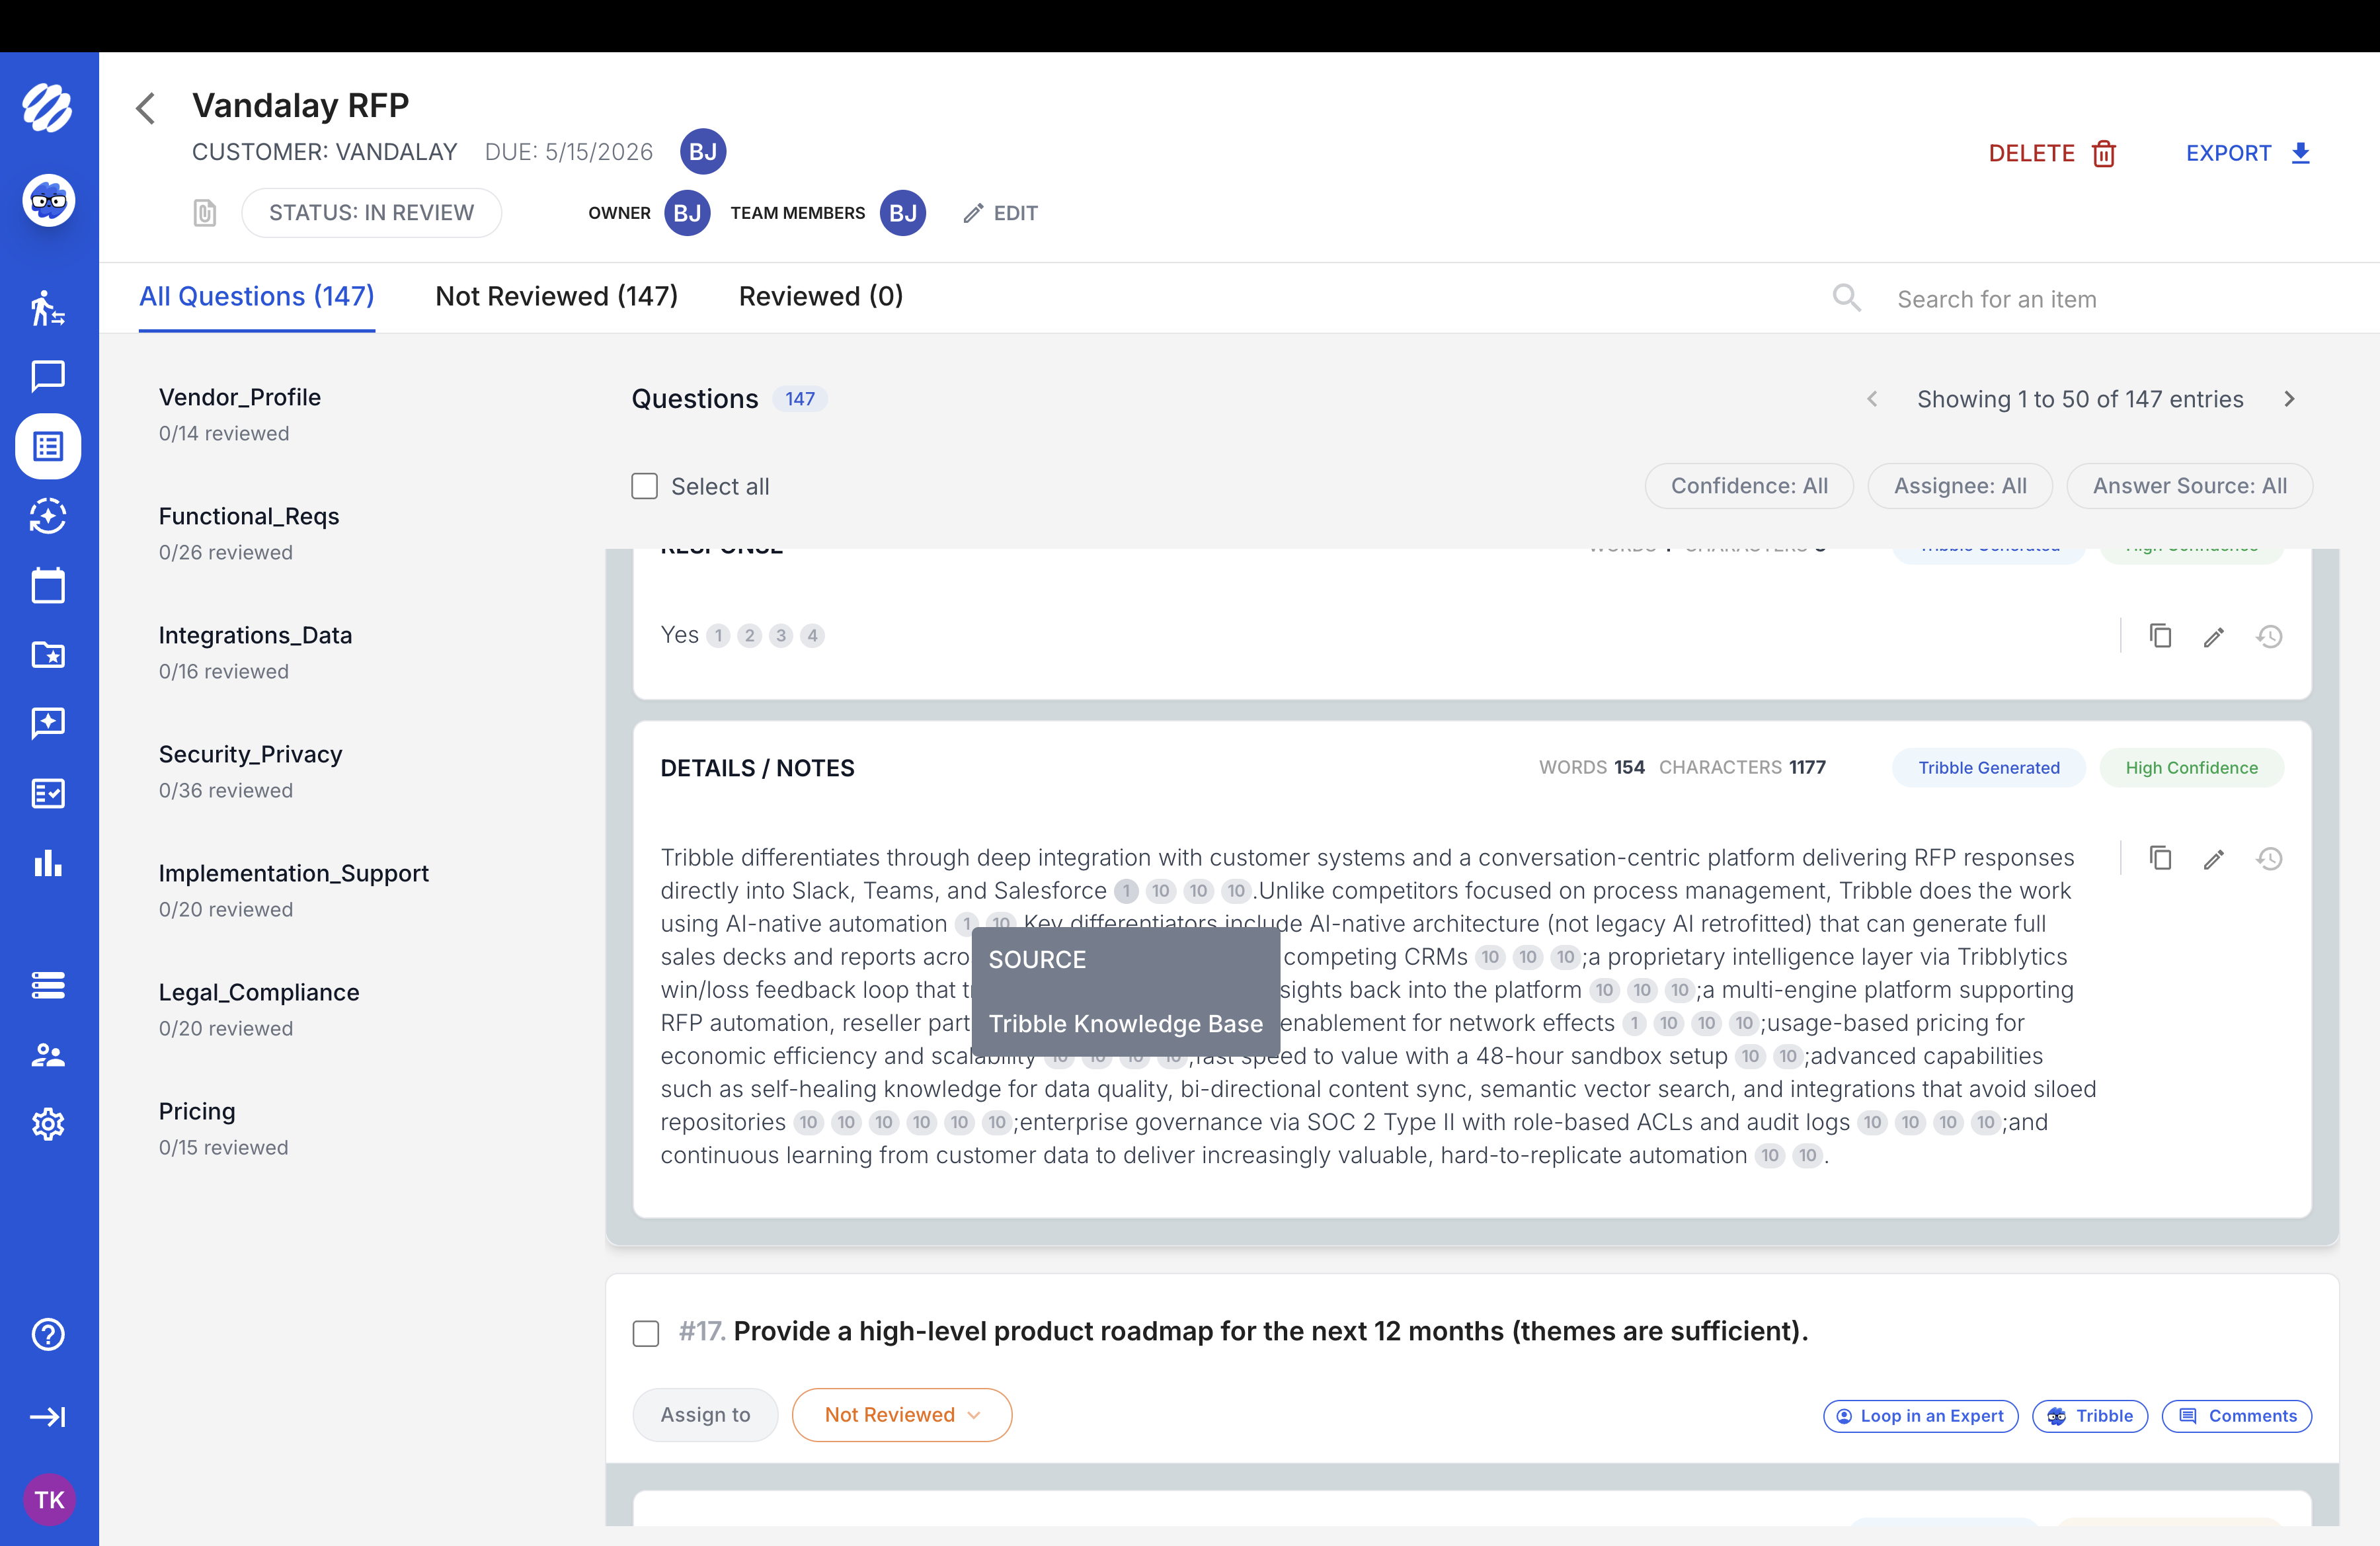
Every answer names the document behind it and how sure it is. It is written for the person assessing you, not as a tidier restatement of their own question.
- 04
Review, and routing for what needs an owner
Confidence decides what reaches a person. Anything your approved content does not cover goes to whoever owns that control, in Slack or Teams, with the question and whatever evidence turned up.
- 05
Consistency check, then submit
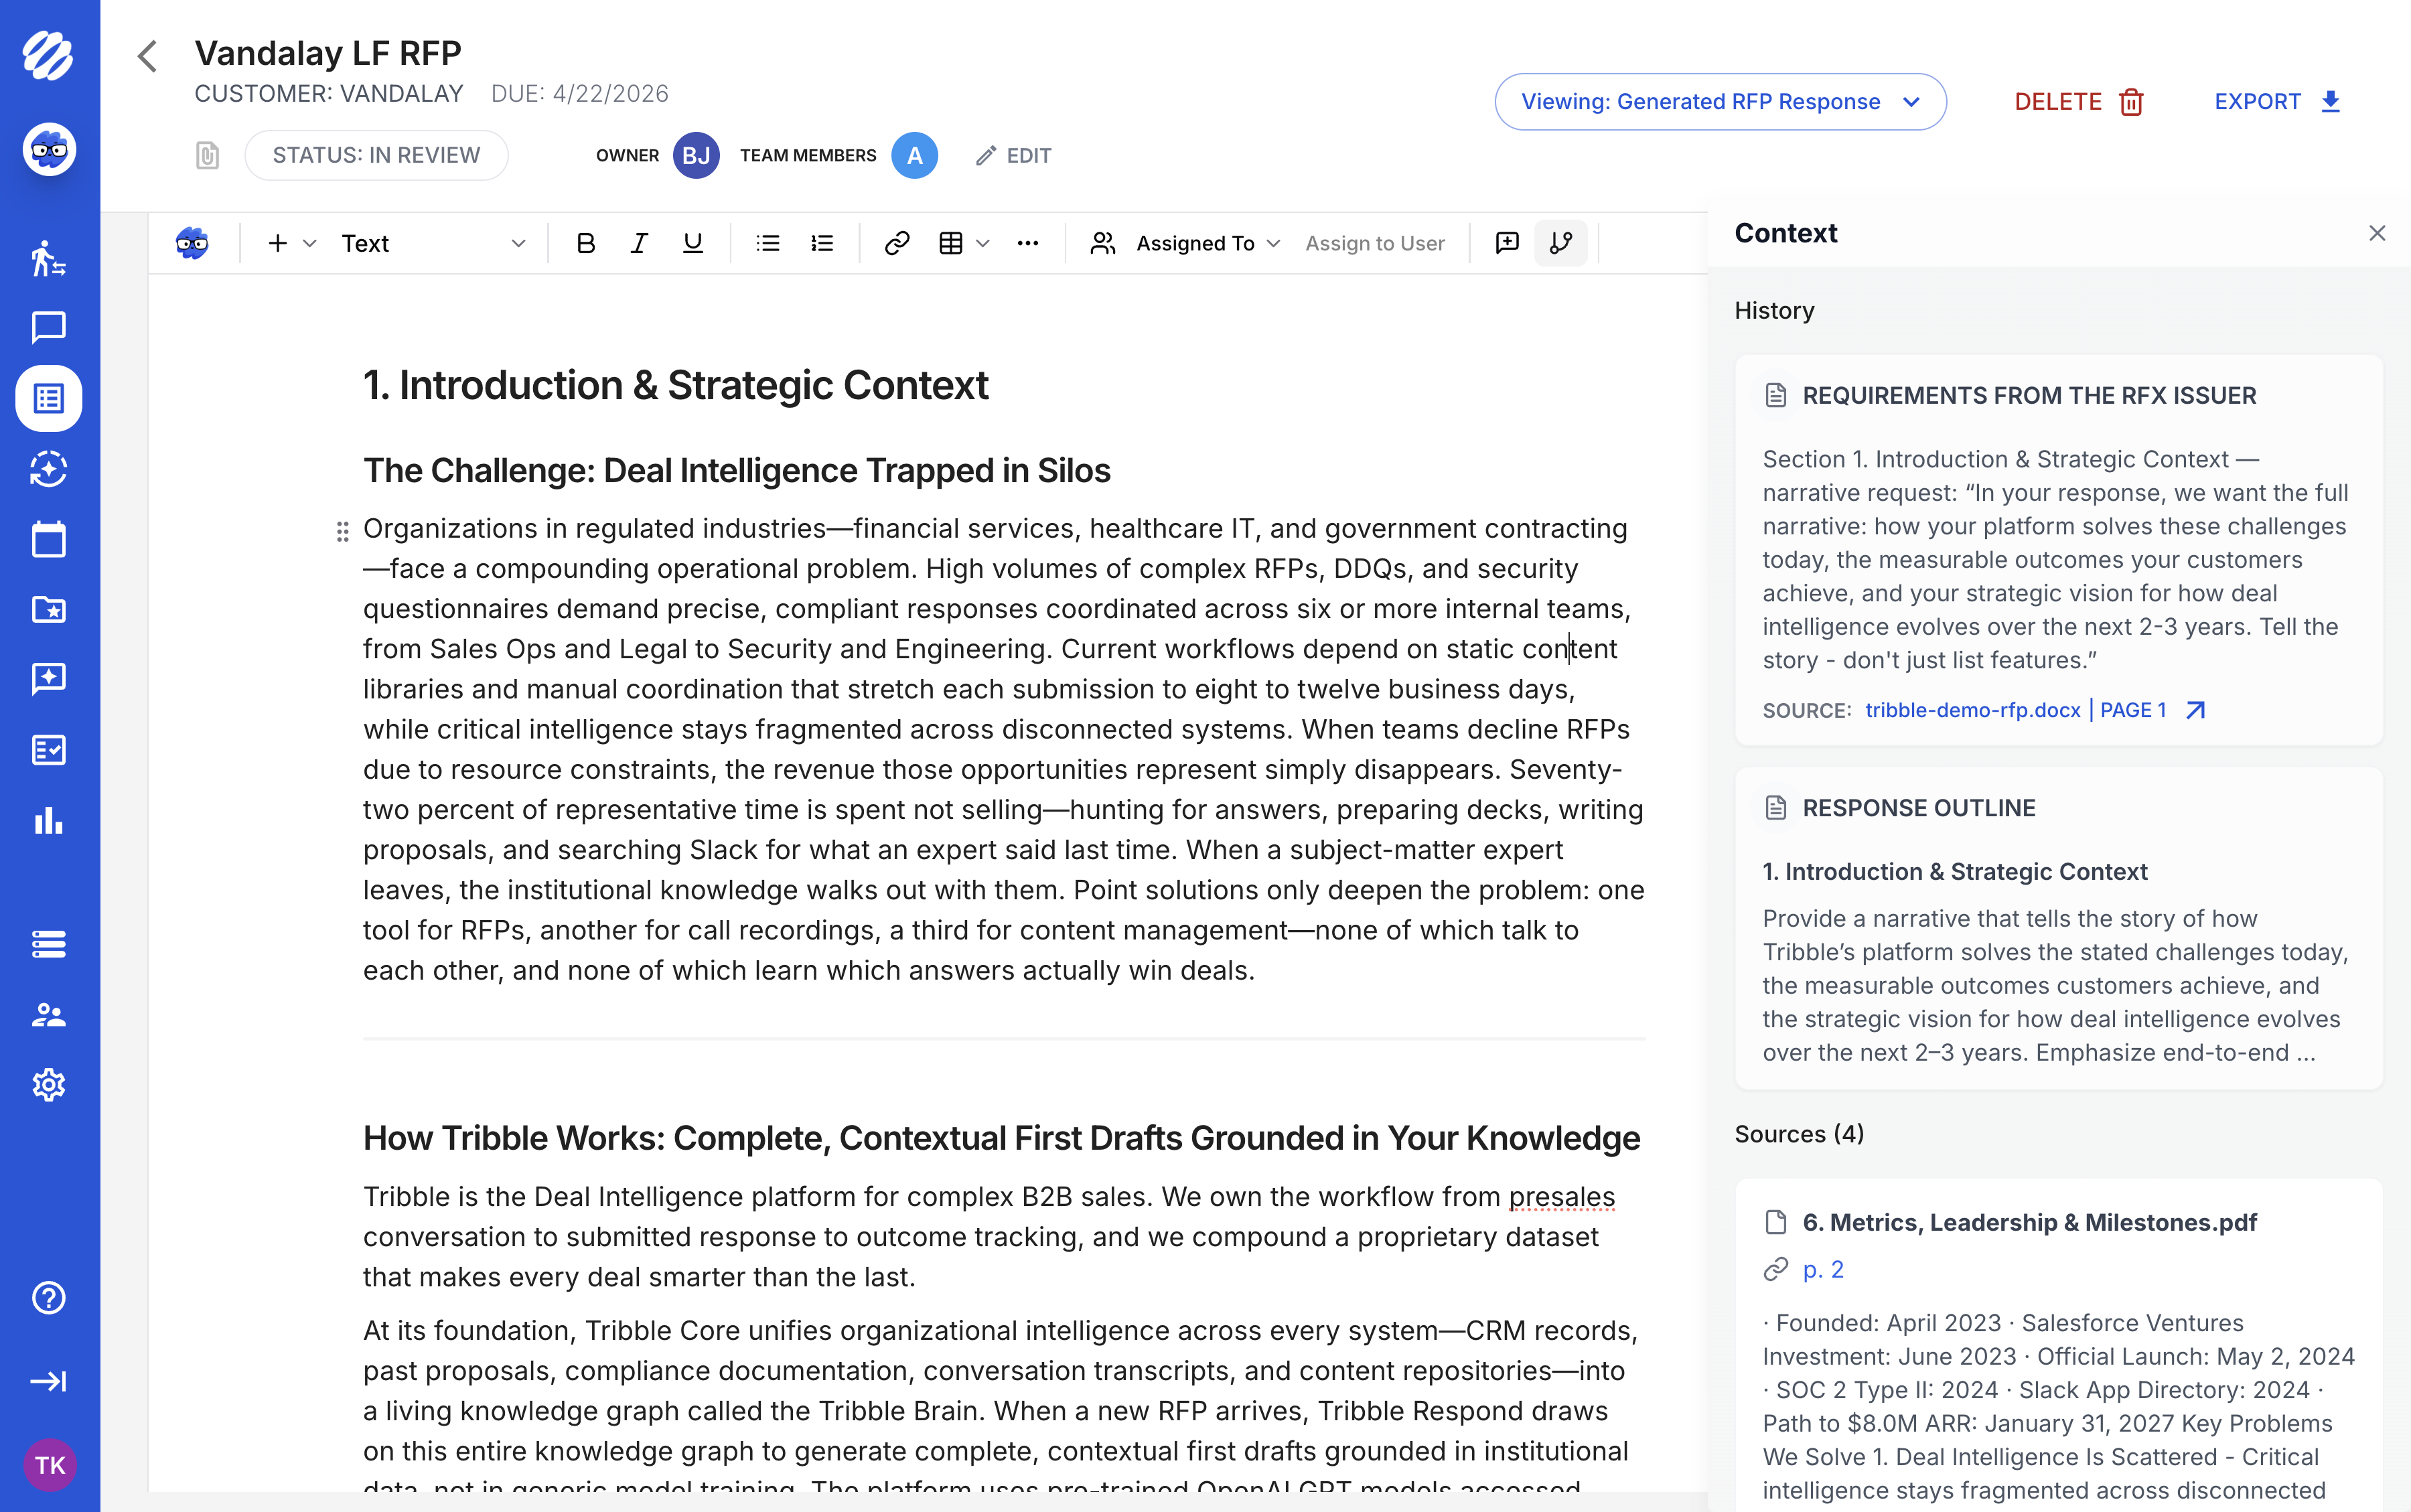
Every answer is read against every other answer, so a contradiction across 200 items turns up here rather than in the evaluator’s notes. What you approve is kept, so the next one starts from it.
The parts that let a reviewer trust a draft they did not write
Reviewing somebody else's draft is slower than writing your own unless you can tell, quickly, which parts to actually read. These are what make that possible.
Per-answer confidence
Each draft says how sure it is, so a reviewer reads the twenty that need them rather than all two hundred at the same depth.
Cross-answer consistency
Every answer is read against every other one. A contradiction across two hundred items turns up here, not in the evaluator's notes.
Buyer-aware drafting
The draft is written for what this evaluator is assessing, rather than restating their own question back at them.
Permission-aware retrieval
Access follows the permissions you already have. Evidence a reviewer cannot open never appears in a draft they can.
Approved answers are kept
Once a reviewer approves an answer it becomes approved content, and the next questionnaire starts from it rather than a blank page.
SIG, CAIQ, or the spreadsheet a buyer built themselves
There is no template to match, because what gets read is the questions and not the layout around them.
The six sections that generate the most back and forth
Most of a questionnaire is answerable from what you have already written down. These are the parts where the evidence exists but the wording decides whether the answer survives review, and they are where step 4 routes most of its questions.
Access control
"Do you support SSO, role-based access and periodic access reviews, and how fast is a leaver removed?"
The answer comes from your access control policy and the CC6 section of the SOC 2 report, which is where an auditor already tested it. Naming the control rather than paraphrasing it lets the evaluator check the claim against the report they have probably already asked for.
Where it goes wrong. Answering yes to SSO when it is SAML on the enterprise tier only. The question is about the plan the buyer is on.
Encryption and key management
"What is encrypted at rest and in transit, with what, and who holds the keys?"
Your encryption standard and the architecture document behind it. The useful answer names the algorithm, the data stores it covers and the key custody model, because those are three separate questions wearing one.
Where it goes wrong. Stating AES-256 at rest without saying which stores it covers, or implying customer-managed keys when the keys are provider-managed.
Business continuity and recovery
"What are your RTO and RPO, and when did you last actually test them?"
The BCDR plan gives the targets and the last test report gives the evidence. An evaluator who asks the second question has usually been given the first one before and found it was aspirational.
Where it goes wrong. Quoting the RTO from the plan rather than from the last real exercise. If those two numbers differ, say so and give the date.
Subprocessors
"Who are your subprocessors, where do they process, and how much notice do we get before the list changes?"
The subprocessor list and the notification period in the DPA. These two drift apart more than any other pair of documents, because the list is maintained by one team and the DPA by another.
Where it goes wrong. A public subprocessor page that is out of date against what the DPA commits to. The buyer checks both.
Incident response and notification
"How quickly are we told about a breach, and what counts as one?"
The incident response plan for the process and the DPA notification clause for the commitment. The questionnaire usually wants a number of hours and the contract usually says without undue delay, so the honest answer gives both and explains which one governs.
Where it goes wrong. Answering with the plan's internal escalation time as if it were the customer notification commitment.
Data residency and transfer
"Where is our data stored and processed, and under what transfer mechanism?"
The architecture document for storage and processing, the DPA and SCCs for the transfer basis. Residency questions are increasingly two questions: where the data sits, and who can reach it from elsewhere.
Where it goes wrong. Saying EU data stays in the EU while support and engineering access it from outside. Access is processing.
None of this is unique to a SIG. The same six run through CAIQ, a VSA and most buyer-built spreadsheets, which is why an answer approved once is worth keeping.
10-20% of security responses needed specialist review
The rest came back from approved content.
Your stack proves the posture. Someone still writes the answers.
Most security teams already run at least one of these, and should. Each is good at the job it was built for. None of them is built for the questionnaire itself, so it comes back to a person every time.
| Tribble | A compliance platform | A content library | General-purpose AI | |
|---|---|---|---|---|
| Who it is for | Teams answering the questionnaire | Teams proving the posture | Teams storing approved answers | Anyone drafting text |
| Source named on each answer | The document it came from | Not its job | Manual reference | None |
| Per-answer confidence | Every draft says how sure it is | |||
| Routing to the control owner | By control area, in Slack or Teams | Alerts on controls | Alert-based | None |
| Consistency across the questionnaire | Checked against every other answer | |||
| Improves with each questionnaire | Approved answers kept and reused | Not its job | Library needs upkeep | No memory between sessions |
A compliance platform and Tribble are complementary, and most teams running one still answer questionnaires by hand. One is the system of record for your posture. The other answers the questionnaires that follow from it.
What happens when a claim is challenged
An out-of-date policy, or a certification scope remembered slightly too generously, is enough to fail an assessment and send procurement back to the start. These are the three questions that do it, and what you can put in front of them.
"Where did this answer come from?"
The policy, the control, or the response you gave the last buyer who asked. Named on the answer itself, not gathered into a reference list at the end of the document. The evaluator gets a document rather than an assurance.
"Does your certificate actually cover that?"
Scope is taken from the report rather than paraphrased, so an answer cannot quietly widen what a certificate covers. This is the one that costs the most, and it is almost always a wording problem rather than a control problem.
"Who signed this off?"
The reviewer and the date, against that answer. If a claim turns out to be wrong, the question becomes which evidence was current at the time, which is answerable, rather than who typed it, which is not.
Where your approved content does not cover a question at all, it is routed rather than filled. An unanswered question sitting with a control owner costs a day. A confidently wrong one can cost the deal.
Where the evidence already lives
Nothing moves into a new system. Policies and evidence stay where they are, deal context comes from the CRM, and the questions that need a person arrive in Slack or Teams.


Questions people ask before a first questionnaire
The ones that come up on nearly every call.
How do you automate security questionnaire responses?
Upload the questionnaire in any format. Each question is classified by control area and matched to approved security content: policies, SOC 2 evidence and prior responses. The draft comes back with the source document named on each answer and a per-answer confidence level. Reviewers verify sourced evidence rather than unattributed output, anything the approved content does not cover is routed to the control owner, and a consistency check runs across the whole questionnaire before submission.
What questionnaire formats are supported?
SIG Lite, SIG Full, CAIQ, VSA, XLSX, DOCX, PDF, and direct portal intake. The question and answer structure is parsed automatically regardless of format, so a buyer's own spreadsheet works the same way as a standard framework.
How is this different from a compliance platform?
A compliance platform collects evidence and monitors controls. It is the system of record for your posture. This answers the buyer questionnaires that follow, by drafting from that evidence, your policies and your prior responses. The two are complementary, and most teams running one still answer questionnaires by hand.
How do you know the answers are right?
Every answer names the document it was drafted from and carries a confidence level, so a reviewer approves a sourced answer rather than an assertion. Answers the approved content does not cover are flagged rather than guessed, and the consistency check catches contradictions across the questionnaire before anyone outside sees it.
What does it connect to?
The places security evidence already lives: SharePoint, Google Drive, Confluence, Notion and Box for policies and evidence, Salesforce and HubSpot for deal context, and Slack and Microsoft Teams for routing questions to the control owner.
Can it answer SOC 2 questionnaire responses?
Yes, where your SOC 2 report and the policies behind it are connected as approved sources. Answers cite the specific control, for example CC6 for access control, so a reviewer can check the claim against the report rather than take it on trust.
What happens to questions nobody has answered before?
They are routed, not guessed. The question goes to the control owner in Slack or Teams with the context and whatever evidence was found, and once they answer it the response is kept as approved content for the next questionnaire.
How long does onboarding take?
A team can run a real questionnaire as soon as source access is connected and the first evidence is indexed. The quality of the first draft depends on how much approved content exists, not on how long the system has been running.
How does pricing work?
Priced per Seller and per Project rather than per questionnaire. The right model depends on questionnaire volume, hours per review and how much work moves from drafting to verification, so we price against your volumes on the call rather than putting a figure on a page.
Read next
Tribble Respond is the product this workflow runs on, alongside RFPs, long-form responses, DDQs and portal intake. DDQ automation is the same workflow against due diligence questionnaires. The guide to security questionnaire automation covers the category rather than the product.